
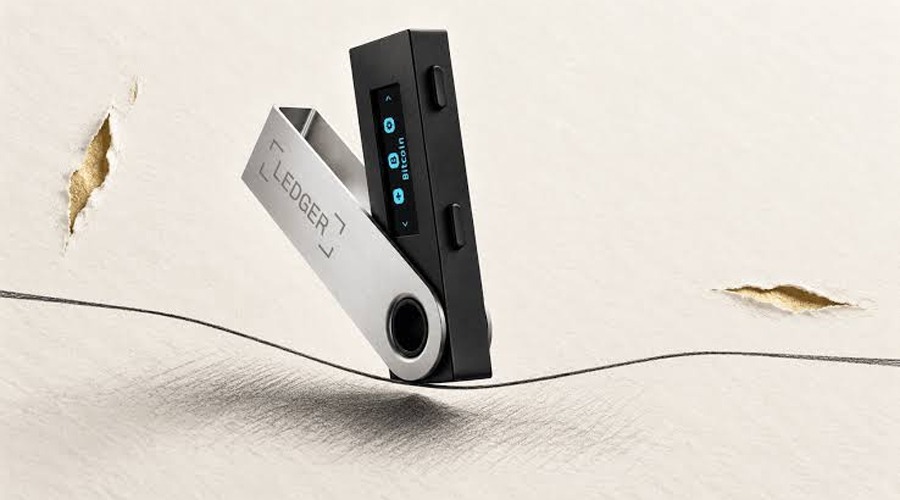
Singapore police have reported about SGD 3.5 million in cryptocurrency losses after customers purchased tampered Ledger hardware wallets from local retailers.
According to an October 28 advisory, the Singapore Police Force (SPF) has received at least two reports involving compromised devices since September 10. Initial investigations found that criminals had fitted the wallets with components capable of stealing sensitive information.
The police have contacted Ledger, which is reviewing the affected cases. However, authorities have not identified the retailers involved or established whether the incidents are connected to other compromised wallets reported across Asia.
Singapore Police Discover Malicious Components in Ledger Wallets
Police investigators found that the affected hardware wallets contained unauthorized components that could capture recovery phrases or private keys. Criminals could then use the stolen information to access cryptocurrency wallets and transfer funds without the owners’ permission.
Hardware wallets normally keep private keys away from internet-connected devices. However, physical modifications can weaken that protection particularly when attackers obtain the recovery phrase used to restore access to a wallet.
The SPF warned users against entering recovery phrases or completing transactions on suspicious devices. It also advised customers to contact manufacturers through official support channels rather than trust unsolicited messages.
Ledger Confirms Hidden Chips in Compromised Devices
The Singapore cases follow an October 13 disclosure from Ledger concerning devices distributed through Southeast Asian reseller CryptoBilis. The company’s Donjon security team discovered hidden hardware capable of capturing the 24-word recovery phrase displayed during wallet setup.
Researchers found that the implant could send the stolen words to attackers through a cellular connection. Moreover, the component operated separately from Ledger’s Secure Element, meaning routine device checks might not detect the modification.
Ledger previously said confirmed thefts in its CryptoBilis investigation involved devices sold through that reseller. However, the company was “also reviewing reports of implants in other signers and locations.” Singapore police have not confirmed a connection between their cases and CryptoBilis.
Ledger Suspends Hardware Wallet Sales Across Southeast Asia
Following the discovery, Ledger asked distributors and retailers to suspend sales across seven Asian markets on October 13. The affected markets included Singapore, Malaysia, Indonesia, Thailand, Vietnam, the Philippines and Hong Kong.
The company also advised CryptoBilis customers who had purchased devices within the previous 90 days to avoid activating unused wallets. Meanwhile, customers who had already initialized their devices were encouraged to move their assets to trusted wallets with newly generated recovery phrases.
The investigation has also reached Europe. German electronics retailer MediaMarktSaturn suspended Ledger sales after reports of a modified device. Ledger said its internal systems and direct sales channels had not been compromised.
Separately, blockchain analysts estimated that wider losses associated with compromised wallets exceeded USD 86 million. However, Ledger said it could not verify the total losses or number of affected customers. Singapore’s SGD 3.5 million figure covers reported local cases.
As investigations continue, Singapore police have urged cryptocurrency holders to protect their wallet credentials. Their advisory states, “Never disclose your private keys, recovery or seed phrases.” Authorities also warned against unsolicited wallet verification and recovery services which could expose users to further theft.
ALSO READ: 10 Crypto Developments Shaping India’s Digital Asset Market
Disclaimer : Crypto News India does not recommend that any cryptocurrency should be bought, sold, or held by you. Do conduct your own due diligence and consult your financial advisor before making any investment decisions.
